

Engineering
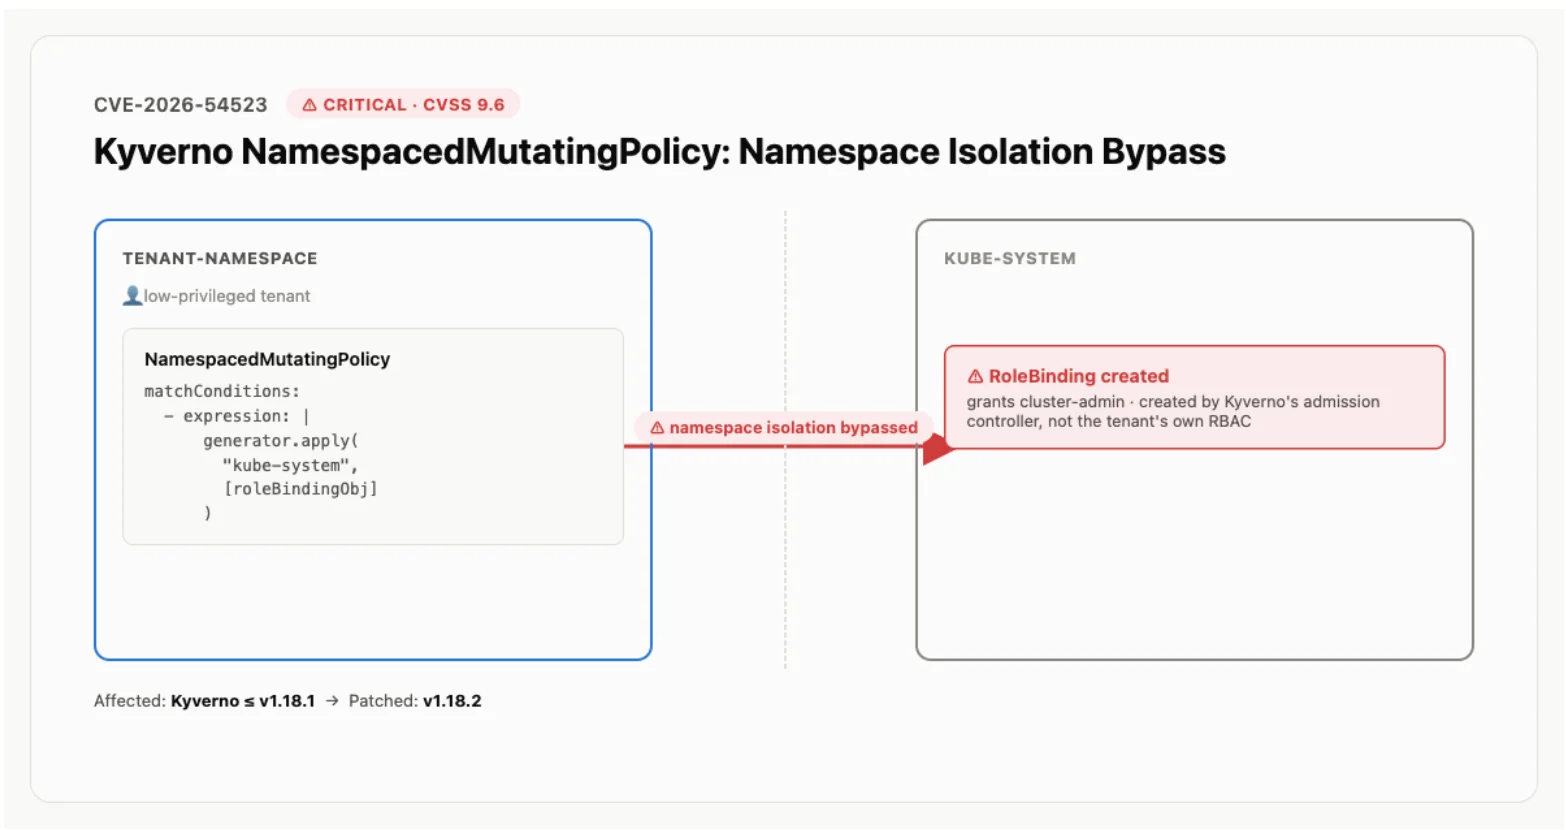
Critical Kyverno Vulnerability — CVE-2026-54523
CVE-2026-54523 (CVSS 9.6) lets a Kyverno NamespacedMutatingPolicy create resources in any namespace. Kyverno 1.18.0 and 1.18.1 are affected; upgrade to 1.18.2.
3 min read
Tag
23 posts
Engineering
CVE-2026-54523 (CVSS 9.6) lets a Kyverno NamespacedMutatingPolicy create resources in any namespace. Kyverno 1.18.0 and 1.18.1 are affected; upgrade to 1.18.2.
3 min read

AI
Quick question: the last time a Kyverno policy rejected a resource, did the error actually tell you why — or did you spend twenty minutes squinting at a pattern block…
6 min read
Events
As an exhibitor and participant at KubeCon 2024, Nirmata was thrilled to engage with the Kubernetes community, share our latest advancements, and experience the energy of…
3 min read
Product
We are announcing a new feature in the Nirmata Control Hub - Offline Cluster Scanning. You can now scan any Kubernetes cluster without installing agents.
2 min read

Product
Designed with security and efficiency in mind, nctl by Nirmata empowers platform engineering and security teams to seamlessly integrate security into their workflows. IaC…
4 min read

Product
Why Ansible is Essential for Modern DevOps In today's fast-paced software development world, automation is crucial for maintaining speed, consistency, and scalability…
4 min read
Kubernetes
Policy-as-code defines security, compliance and operational rules as versioned code that runs automatically. Here are 10 reasons cloud-native teams rely on it.
5 min read

Engineering
AWS CDK: Bringing Flexibility to Cloud Infrastructure The AWS Cloud Development Kit (CDK) is an open-source framework that enables developers to define cloud…
5 min read

Kyverno
Nirmata explores how large financial institutions can leverage policy-as-code, using Kyverno - the Kubernetes-native policy engine - for better governance and security.
4 min read
Kyverno
PolicyReport API The Policy Report API was developed under the Kubernetes Policy Working Group and provides an API that can be used by any policy engine, security…
4 min read
Business
Policy-as-code allows platform engineering teams to define, manage, and enforce policies for security, compliance, and operational requirements. Nirmata explains here.
3 min read

Engineering
Shift-Down Security is complementary to Shift Left Security and is an innovative solution involving seamlessly embedding security measures into Dev workflows and…
3 min read