

Kyverno Open Source
Validate, mutate, and generate resources using Kubernetes-native YAML and CEL across all infrastructure. Easy-to-learn and powered by the CNCF community.
What is Kyverno?
Kyverno is an open‑source policy engine for your entire cloud infrastructure that uses YAML and CEL generated policies that you know and are familiar with. Use Kyverno to validate configurations, mutate them to match standards, and generate required resources automatically.
Why Teams Choose Kyverno
Kubernetes-Native
Policies are custom resources that work along with Kubernetes
Code-to-Cloud Coverage
Apply policies to IaC & CI/CD, enforce in clusters, and check cloud resources
Familiar YAML & CEL
Use common YAML to define a policy and embed CEL expressions to provide validation logic
Flexible Modes
Admission control, background scans, and policy reports
Ecosystem Ready
Works with major Kubernetes distros, CI/CD tools, and cloud platforms
Shift-Left Security
Automate guardrails and validate manifests in CI/CD pipelines
GitOps Friendly
Works with Argo CD and Flux. Great fit for pull-request workflows
Thriving Community
CNCF project with over 3 billion downloads, and active contributors and examples
Core Capabilities
Validate
Enforce best practices, block risky settings, require labels, and ensure images come from approved registries
Mutate
Auto‑insert defaults, annotations, limits, and security settings so resources meet your standards
Generate
Create supporting resources on-the-fly: ConfigMaps, NetworkPolicies, and more—based on rules you define
Report
Continuously scan workloads and produce policy reports to track compliance over time
Get Started
Step 1: Install
Use Helm or kubectl with the quickstart guideStep 2: Try
Import community policy samples and baselinesStep 3: Scan
Run background scans to see current postureStep 4: Enforce
Flip policies from audit to enforce when ready
Common Use Cases
- Pod security standards and baseline hardening
- Blocking latest tags and untrusted registries
- Requiring labels, annotations, and resource limits
- Policy gates in CI/CD and IaC (e.g., Terraform) plans
- Cloud configuration guardrails for accounts, IAM, and networking
- Continuous verification and reporting
Not ready for Nirmata?
Get started with Kyverno and add-on Nirmata when you need enterprise-grade operations and AI‑powered governance.
When to Add Nirmata
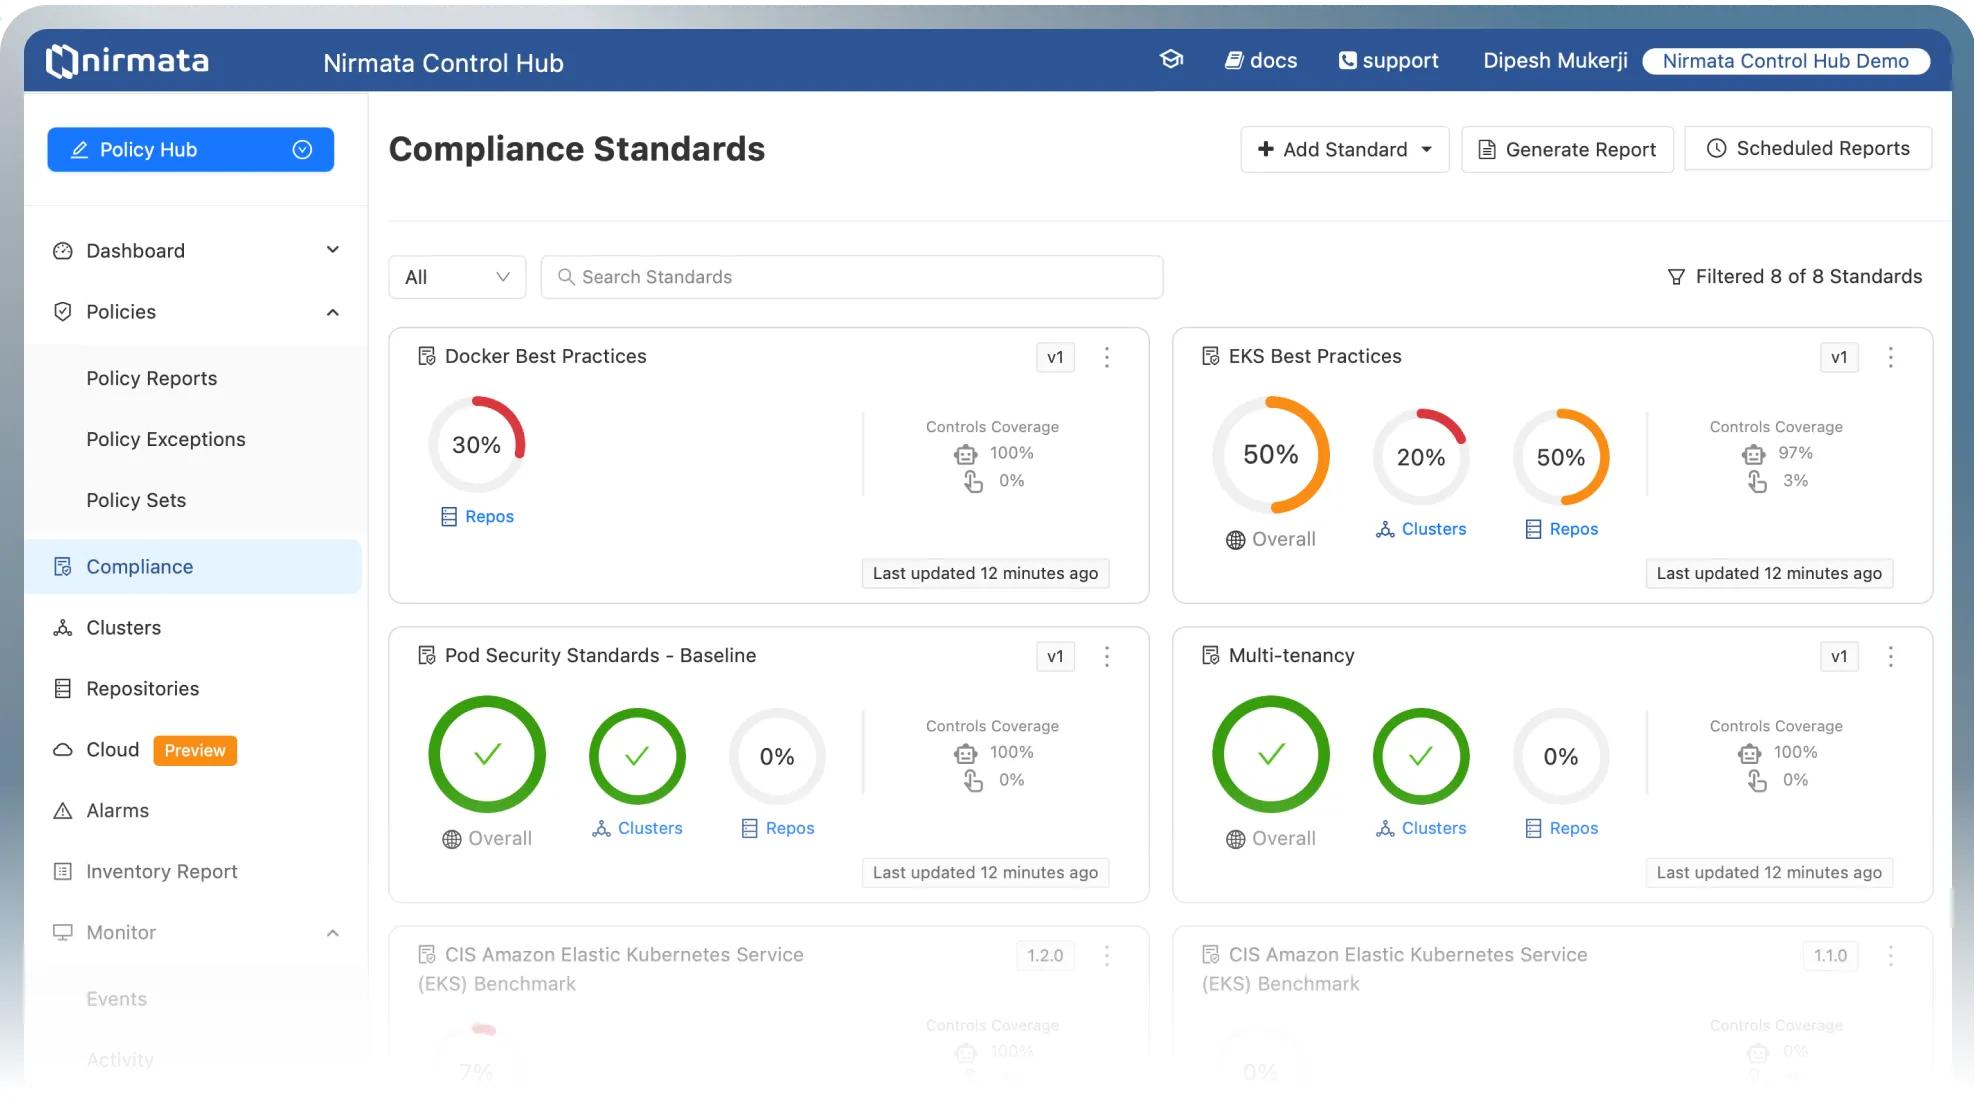
Start with Kyverno and then add Nirmata Enterprise for Kyverno when you want an enterprise-grade lifecycle, health checks, SLAs, and reporting. Further add Nirmata Control Hub when you want a central control layer, dashboards, and AI agents with a natural‑language AI Copilot.
Resources and Community & Support
Resources
- Documentation and tutorials
- Policy sample library
- Release notes and roadmap
- Blog posts and community talks
Community & Support
- Community Slack and meetings
- Office hours and working groups
- Contribution guidelines and good first issues
Proud Member of the Kubernetes Community
Kyverno is a Cloud Native Computing Foundation incubating project built and maintained with the community. Nirmata helps lead the project and provides enterprise‑grade operations and AI‑assisted governance when you need it.
Try Kyverno
Start with open‑source policy‑as‑code in YAML and CEL. When you’re ready to scale and automate, add Nirmata.