



Shadow AI Discovery
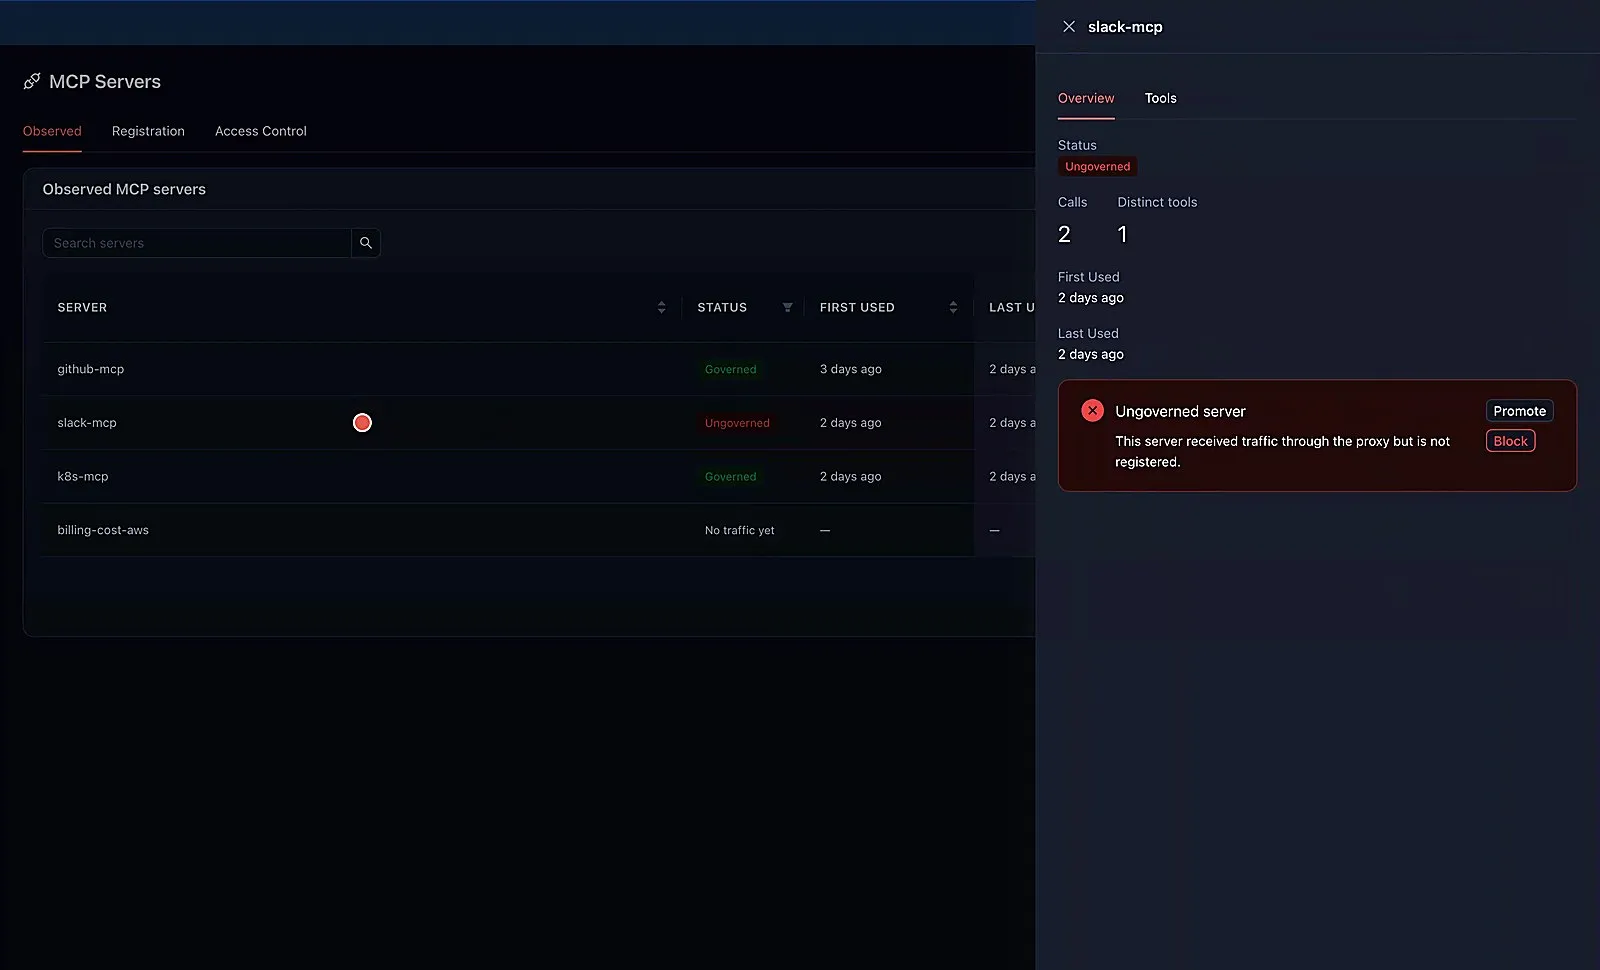
Finds the MCP servers nobody registered.
AIControls builds a live inventory of every server your agents actually talk to — not just the ones your team knows about.
AIControls governs every AI agent and model call in your Kubernetes clusters — enforced by policy, logged for audit.
Switching high-cost model sessions to a lighter model could save ~$1,850/wk
apiVersion: policies.kyverno.io/v1
kind: ValidatingPolicy
metadata:
  name: block-destructive-ops-production
  namespace: nirmata
  annotations:
    proxy.nirmata.io/enforcement-mode: deny
    proxy.nirmata.io/category: Destructive Ops
    proxy.nirmata.io/description: "Blocks irreversible destructive operations (delete, drop, destroy) in production namespaces."
    proxy.nirmata.io/frameworks: "owasp:LLM08,mitre:AML.T0048,nist:MP-2.3,eu-ai-act:Art.9"
spec:
  evaluation:
    mode: JSON
  matchConditions:
    - name: is-destructive-tool
      expression: >
        object.tool.name in [
          "kubectl_delete", "kubectl delete",
          "helm_uninstall", "helm uninstall",
          "terraform_destroy", "terraform destroy",
          "delete_resource", "drop_table", "truncate_table"
        ]
  validations:
    - expression: >
        object.agent.namespace != "production" &&
        object.agent.namespace != "prod" &&
        !object.agent.namespace.startsWith("prod-")
      # The action wording follows object.policy.enforcementMode, so the
      # message never claims an action the gateway does not take in this mode.
      messageExpression: >
        object.policy.enforcementMode == "deny"
          ? "Destructive operations are blocked in production namespaces."
          : (object.policy.enforcementMode in ["warn-approve", "warn-ask"]
            ? "Destructive operations targeting production namespaces require human approval."
            : "Destructive operation in a production namespace.")
    - expression: >
        !object.tool.arguments.exists(k, k == "namespace") ||
        (!string(object.tool.arguments.namespace).startsWith("prod") &&
         string(object.tool.arguments.namespace) != "production")
      messageExpression: >
        object.policy.enforcementMode in ["warn-approve", "warn-ask"]
          ? "Destructive operations targeting production namespaces require human approval."
          : (object.policy.enforcementMode == "deny"
            ? "Destructive operations targeting production namespaces are blocked."
: "Destructive operation targeting a production namespace.")AIControls extends Enterprise Kyverno's Admission control with three additional control points for AI workloads and agents — Pipeline, Gateway, and Runtime — so an agent is governed before it ships, on every model and tool call it makes, and while it runs.
1. Pipeline
Registry · CI/CD · Admission
3. Runtime
eBPF · Clusters · Egress
Powered by Kyverno — the CNCF policy engine your platform team already runs, now governing AI.
The Agentic Control Loop
Deterministic policy decides most calls. A bounded judge decides what's left — the agents only make policy better over time.
Request & Response Scanning + PII Redaction
Requests are checked for identity and privacy before they go out. Responses are checked for cost, security, and policy before they come back — with PII redacted in both directions and a human gated on anything high-risk.
Your AI
AIControls Gateway
What They Reach
Agent Action Graph & Session Replay for Forensics
Not a log to correlate by hand. A graph of who delegated to which agent, every tool it called, every resource it touched — with the policy verdict on each one.
Gateway & Runtime Controls
Governance enforced while the agent is acting, not policy reviewed after the fact. Real screens from AIControls running on real clusters — not hypothetical failure modes.
Shadow AI Discovery
AIControls builds a live inventory of every server your agents actually talk to — not just the ones your team knows about.
Prompt Injection Defense
Most content-safety tools only scan an agent’s outbound request. AIControls scans the response too — catching an attack hidden in a document before the agent ever reads it.

Agent Behavior Anomaly Detection
AIControls baselines each agent’s normal token use, call rate, and prompt patterns, and flags the moment one breaks its own pattern — before a monthly cap would ever notice.

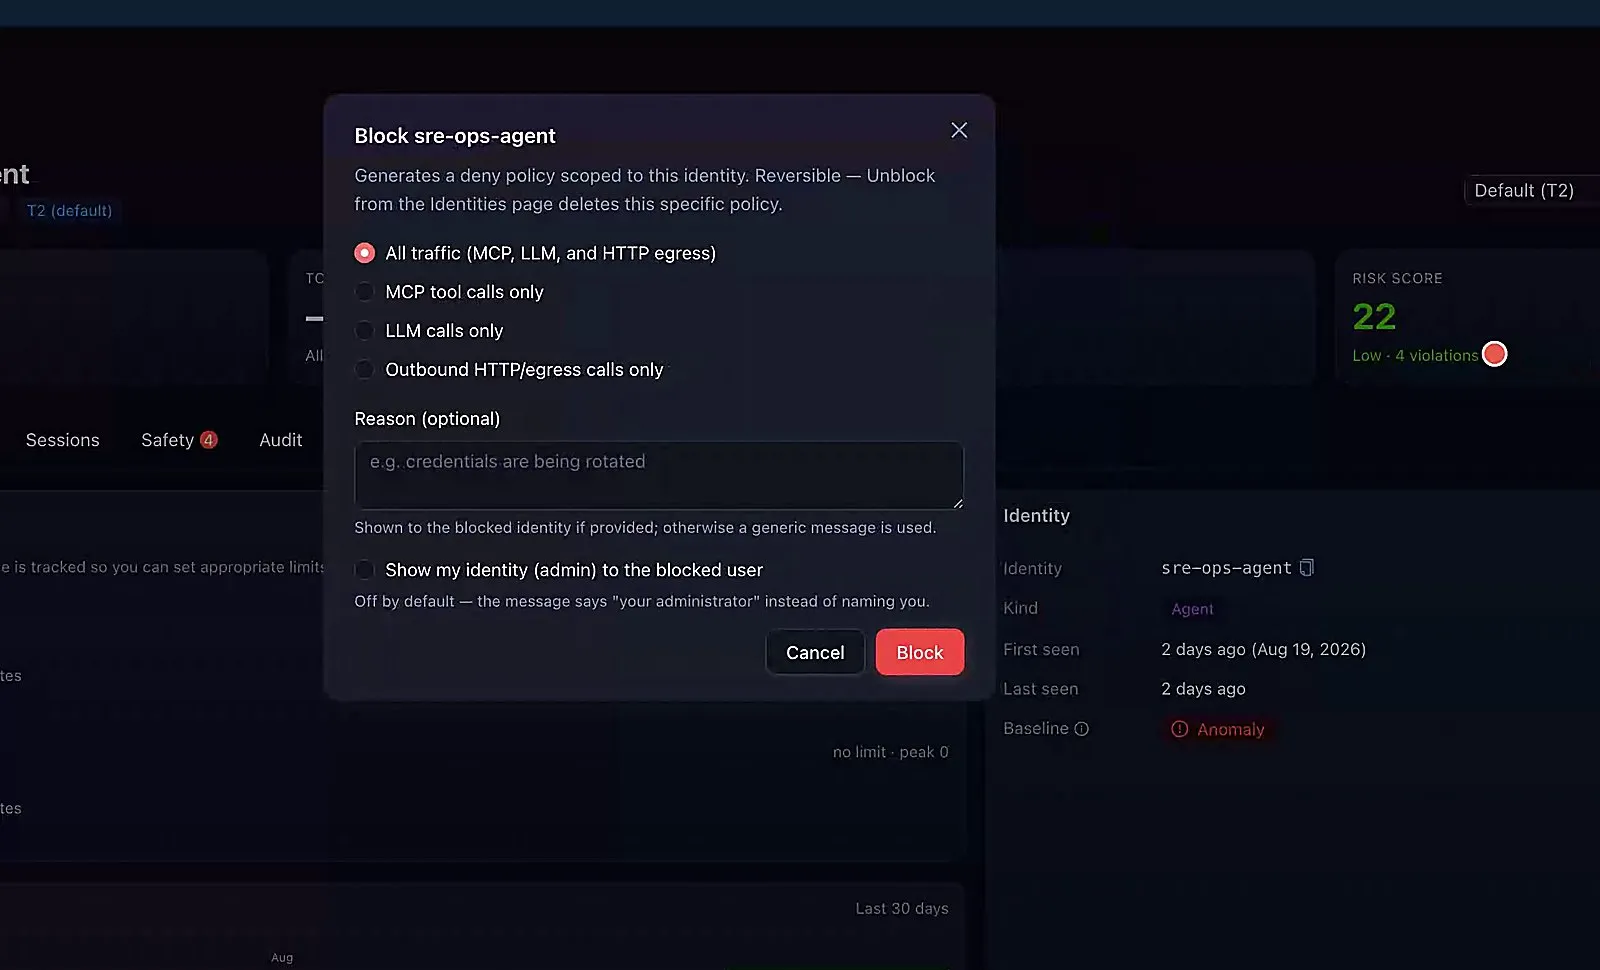
Kill Switch
No policy to write, no deploy to wait on. Scope it to all traffic, MCP only, LLM only, or just egress — and fully reversible.
Human in the Loop
A hard cap either blocks real work or gets overridden under pressure. AIControls holds the request for a named approver instead — decision on record, no ticket thread.

Identity your IdP already issues, enforcement your auditors already understand.
Identity provider
Who is this agent, and what is it entitled to reach?
AIControls · Gateway & Runtime Controls
What is the agent doing right now — and should it be allowed to proceed?
Design partner
“We were already writing Kyverno policies for our clusters. Governing AI agents turned out to be the same language and the same approval process, which is why this took days rather than a quarter.”
Also in AIControls
Risk scoring, identity, cost control, and MCP governance — the controls that round out AIControls Gateway.
Composite risk per agent, trust score per tool; cross a threshold and the Kill Switch is one click away.
Developer, workload, or delegated agent — verified via your IdP.
Spend attributed to team, user, and model as it happens; budgets enforced before overrun.
Per-tool and per-datasource policy, argument validation, discovery scoped to identity.
Deploy inline as your LLM/MCP gateway, or as an ext_proc filter in front of Envoy or LiteLLM. HA, PostgreSQL-backed, running in under 30 minutes.
Read the full data sheet (PDF)A short working session on your own clusters — no agent changes, no code changes, nothing enforced until you decide it should be.