


Kyverno
Kyverno 1.19.2 Security Release: 26 Advisories Fixed
What the 26 advisories in Kyverno 1.19.2 mean for your clusters: tenant escapes to cluster admin, image verification bypasses, checks to run, how to upgrade.
8 min read
Tag
15 posts
Kyverno
What the 26 advisories in Kyverno 1.19.2 mean for your clusters: tenant escapes to cluster admin, image verification bypasses, checks to run, how to upgrade.
8 min read

Engineering
Shift-Down Security is complementary to Shift Left Security and is an innovative solution involving seamlessly embedding security measures into Dev workflows and…
3 min read
Business
Traditionally, security teams operated as gatekeepers, enforcing security at the end of the development cycle. However, this approach is no longer sufficient.
5 min read

Engineering
Introduction In our previous blog post, we delved into the importance of addressing CVEs within application libraries and outlined strategies for remediation. Continuing…
5 min read
Events
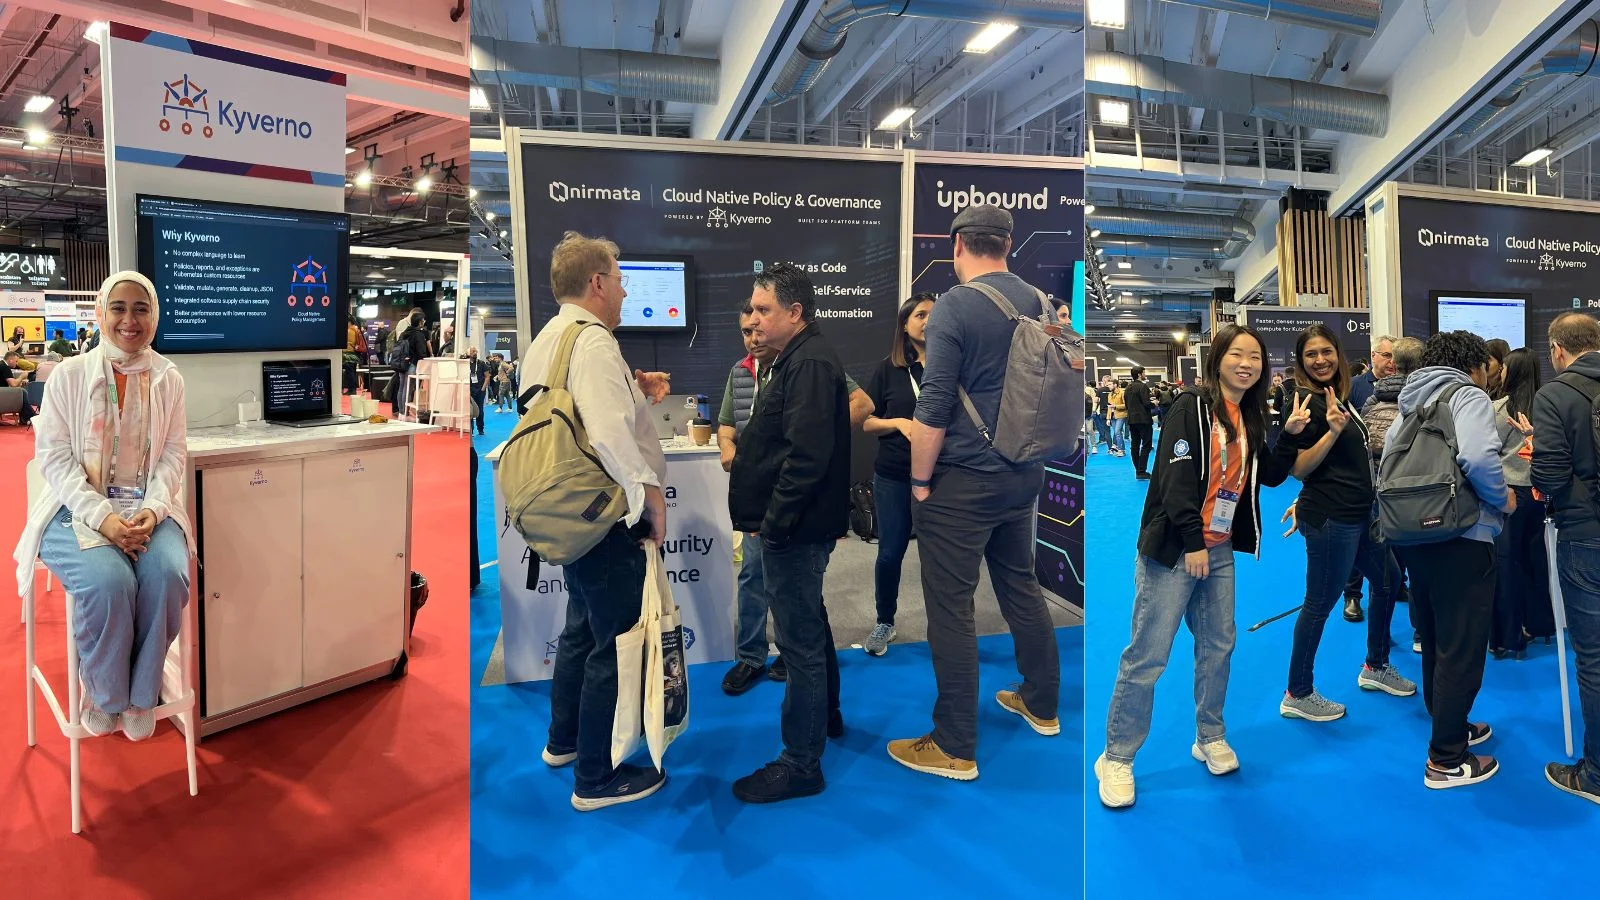
This year, KubeCon + CloudNativeCon Europe 2024 drew over 12,000 tech enthusiasts from the leading cloud native and open source communities, and celebrated the milestone…
4 min read

Product
Preventive security stops misconfigurations before deployment, while detection and response catches threats at runtime. How they differ and why you need both.
4 min read

Product
The shift from reactive to proactive measures marks a significant paradigm change for application security. This transformation is pivotal in the way organizations…
3 min read
Engineering
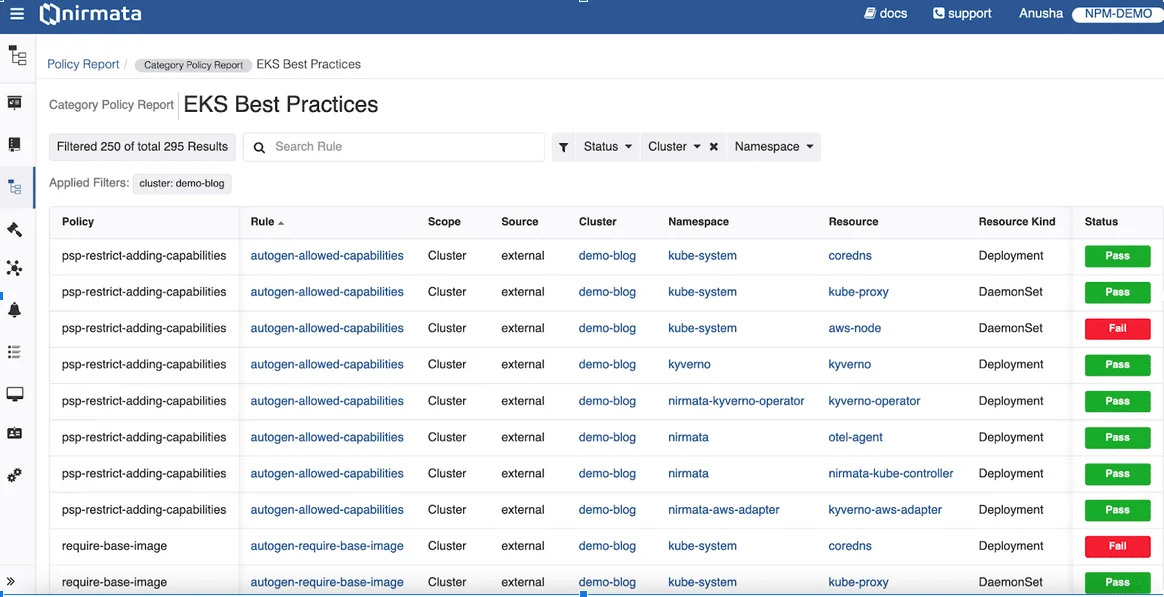
AWS provides suggestions to secure Amazon EKS clusters, but it’s crucial to enforce best practices and prevent misconfigurations to avoid unintended attacks. Kyverno by…
8 min read

Kyverno
Nirmata announces the open-source release of Nirmata AWS Adapter for Kyverno, making key cloud configuration info available for policy enforcement and helping to automate…
6 min read

Business
Platform teams implement policy-based guardrails for Kubernetes environments on Day-0 to avoid resets, unexpected costs and downtime. Nirmata explains here.
5 min read
Engineering
Kyverno product release v1.6.0 focuses on providing for use cases and policies around Kubernetes security, policy and governance. Nirmata explains more here.
6 min read

Engineering
CVE-2021-25742 lets ingress-nginx users with Ingress access read all cluster secrets via snippets. Upgrade to v1.0.1 or v0.49.1 and disable snippet annotations.
3 min read