

Newsletter
Nirmata Pulse: October 2026
Governance Beyond the Admission Webhook
News from Nirmata, October 2026
Kyverno reviews workload requests before the Kubernetes API server accepts them. That position is what makes policy-as-code effective, and it is also why the policy engine itself now needs hardening.
September brought that into focus: a threat model built with the CNCF and the Kyverno maintainers, a security-focused Kyverno patch, policy checks that run before infrastructure is applied, and the final weeks before KubeCon North America.
Here’s what changed this month.
THE BIG STORY
Kyverno guards your cluster. Who is guarding Kyverno?
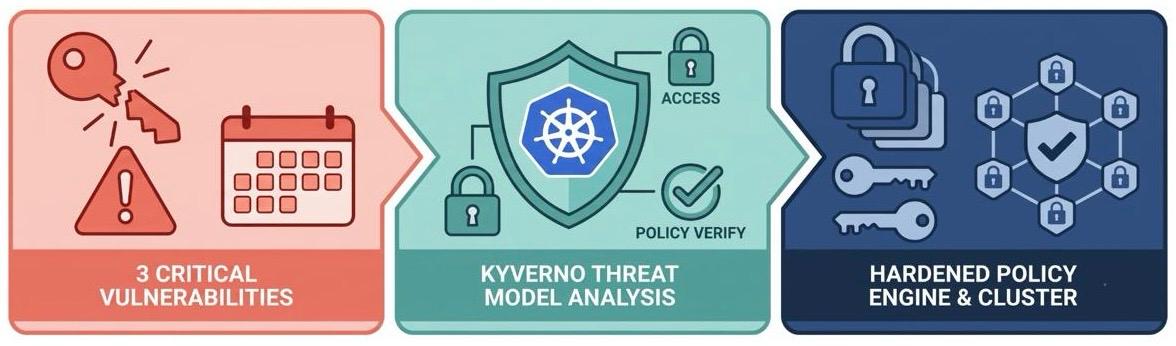
Three critical Kyverno vulnerabilities were disclosed within six months, highlighting the need to harden the policy engine itself. The Kyverno End User Threat Model and Hardening Guide outlines key risks around fail-open configurations, image verification, policy integrity, and RBAC.
Read the full hardening guide to learn more.
THIS MONTH AT NIRMATA
⚙️ SHIFT-LEFT GOVERNANCE
Enforcing Policy Before the Terraform Apply
A Terraform change can pass code review and still introduce security risks after apply.
Beyond the Merge shows how to scan Terraform plans with nctl, catch issues like public S3 access and wildcard IAM permissions, and manage exceptions as reviewable PolicyException YAML files.
🛡️ ENTERPRISE KYVERNO
CVE Fixes for Every Supported Release
When a critical CVE lands, upgrading every Kyverno cluster immediately isn’t always practical. Nirmata Enterprise for Kyverno (N4K) provides backported CVE fixes, 18 months of patch support per release, and 24/7 enterprise support with SLAs, while remaining compatible with Kyverno OSS.
FROM THE KYVERNO ECOSYSTEM
Kyverno 1.19.1 Ships Security Fixes
Kyverno 1.19.1 addresses several security issues, including a PolicyException scope bypass, an IPv6 blocklist bypass, and Go vulnerabilities. It also adds autogen support for custom workload CRDs.
ClusterPolicy Is Deprecated. Plan Your Migration.
Kyverno 1.19 deprecated the legacy ClusterPolicy and Policy types, with removal planned for 1.20. Teams should start planning migration to the new CEL-based policy types.
Guardrails, Not Gates
Kyverno can go beyond blocking deployments. Mutation and generation can apply safe defaults automatically, helping platform teams reduce rejected deployments and create smoother developer workflows.
THE ROAD TO KUBECON
KubeCon + CloudNativeCon North America 2026
November 9 -12, 2026 · Salt Lake City, Utah
KubeCon North America brings the cloud native community together for keynotes, technical sessions, and discussions on Kubernetes, security, platform engineering, and AI infrastructure.
- November 9: Co-located events, including Agentics Day, Open Source SecurityCon, and Platform Engineering Day.
- November 10 -12: Main conference sessions, the Solutions Showcase, AI Inference + Agentic track, and Kyverno-related Maintainer Track sessions.
Join with us at Salt Lake City, November 9 -12, at Booth 278 in Hall 4. Meet the Nirmata and Kyverno teams to explore enterprise Kubernetes policy, security, and governance in action.
Dates to Know
October 5 - November 6 : Security Slam 2026: Fall Edition 30-day open source security improvement challenge.
October 11 : KubeCon Europe 2027 CFP closes
November 9 : KubeCon North America co-located events, including Agentics Day
November 10 - 12 : KubeCon + CloudNativeCon North America in Salt Lake City.
STAY AHEAD OF KUBERNETES GOVERNANCE
The latest thinking around Kyverno, AI governance, runtime security, and policy-as-code.
Explore our Projects on GitHub to see the latest developments and contribute [GitHub].